
Fraud Intelligence Guide
Malicious Automation and Botnet Signals
Identify the repeated action and the business cost.
By Michael Joseph · Last updated: October 23, 2026
What to understand
Automation becomes an abuse concern when it scales an action in a way that harms the service or its users. Registration, messaging, payment attempts and resource requests each create different problems. A bot assessment is most useful when it identifies the workflow under pressure and the decision that could interrupt the harm.
Look across distributed activity
A coordinated operation may use many devices or connections. Compare repeated sequences, timing and targeted actions instead of relying only on one IP address. Botnet-related activity requires corroborating evidence; a shared traffic pattern alone cannot establish that every participating device or person is malicious.
Signals to review together
Registrations, forms, payments, and content requests can each become targets.
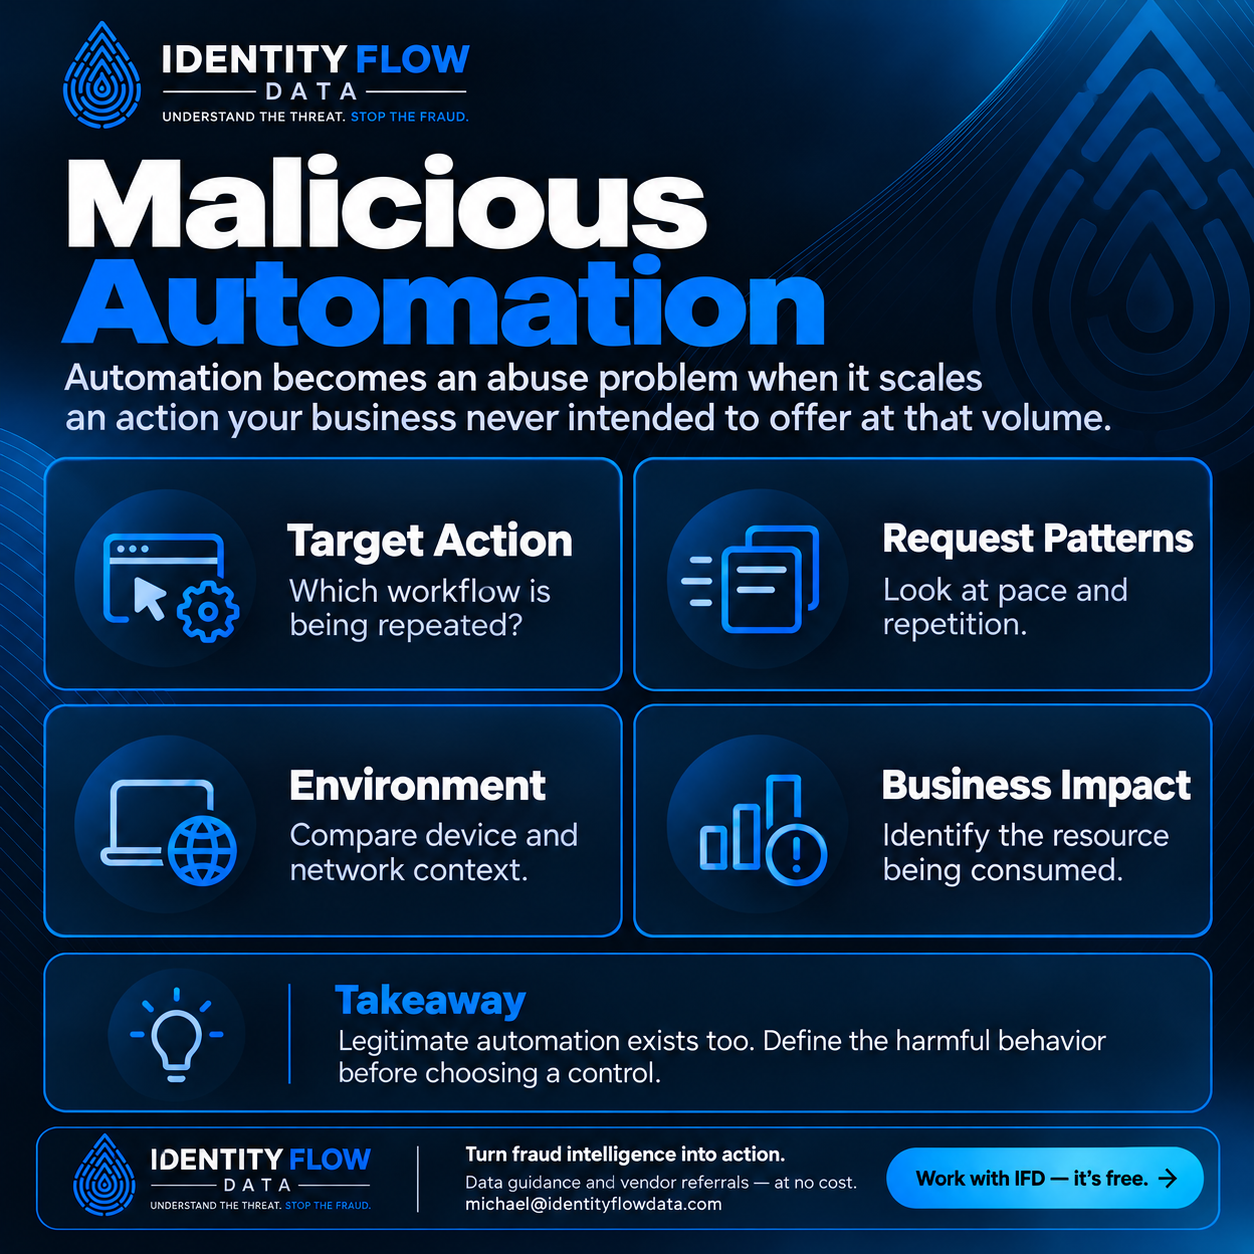
- Target Action: Which workflow is being repeated?
- Request Patterns: Look at pace and repetition
- Environment: Compare device and network context
- Business Impact: Identify the resource being consumed
Measure the effect on the workflow
Separate legitimate integrations, accessibility tools and expected traffic surges from harmful requests. Assess completion quality, resource consumption and operational burden. Evaluate controls against real outcomes and monitor whether the activity shifts to a different step after a change.
Botnet Activity
Compromised devices can be coordinated to generate abusive traffic while spreading activity across many sources.
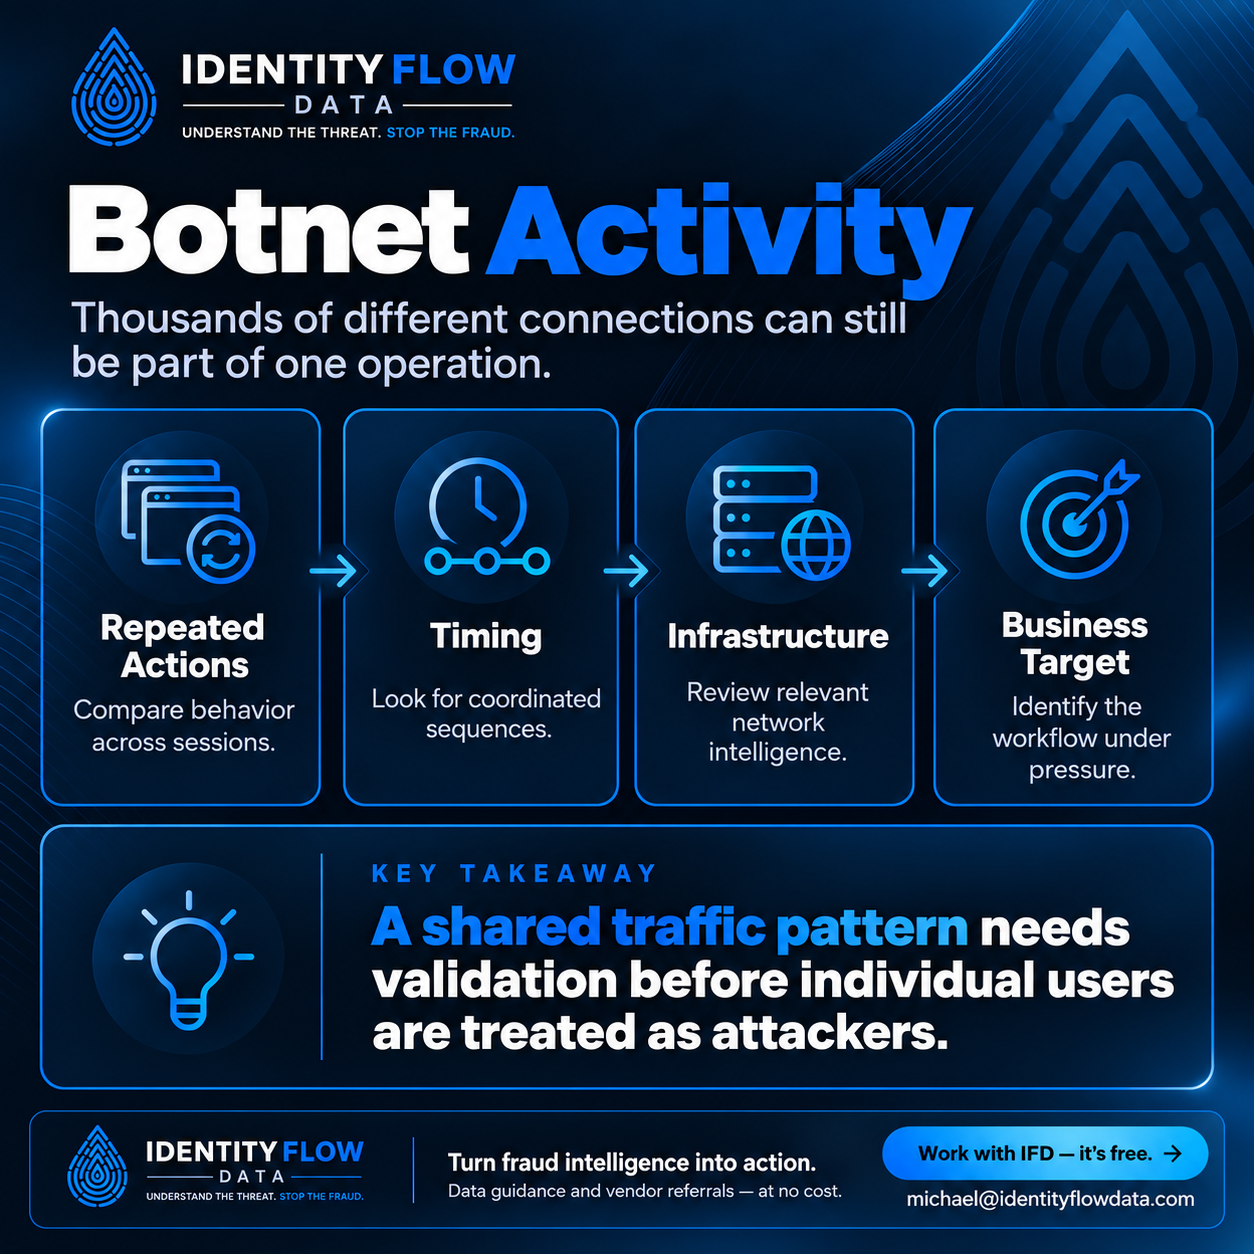
- Repeated Actions: Compare behavior across sessions
- Timing: Look for coordinated sequences
- Infrastructure: Review relevant network intelligence
- Business Target: Identify the workflow under pressure
Keep legitimate activity in view
Legitimate automation exists too. Define the harmful behavior before choosing a control.
How IFD can help
Tell us which decision you want to improve and what evidence your team already has. IFD helps clarify useful signals, compare suitable providers and scope an evaluation. We review coverage, limitations and practical fit so your team can decide on the next step.
Common questions
Choose your starting point with IFD.
Understand your business’s exposure
Request a scoped review of relevant underground activity and fraud techniques involving your business. No customer dataset required.
Request a Free Exposure ScanEvaluate your fraud data
Discuss a sample evaluation of relevant fraud and identity signals. No IFD coordination fee; scope and any provider charges agreed first.
Request a Data EvaluationThere is no advisory fee for buyers. IFD is compensated by participating providers when a qualifying purchase results from a referral. We explain applicable arrangements upfront. Any provider testing or product charges are confirmed before you proceed.
Related guidance