
Understand the network behind the activity.
Evaluate IP reputation, network classification, and available proxy-detection signals for your registration, login, lead, and transaction flows. IFD helps you assess coverage, test relevant data, and compare providers—with no advisory fee for buyers.
What IP intelligence can reveal
Approximate geolocation
Country, region, and city-level estimates based on network registration data. Geolocation does not establish a person's precise location—it reflects where the IP block is registered, which may differ from the user's actual location.
Network owner and classification
The organization or ISP that owns the IP block, and whether it is classified as residential, mobile, hosting, or data center. Network classification is distinct from proxy detection—a residential IP can still be intermediated.
Reputation and observed-abuse indicators
Some providers return signals based on observed abuse history, spam reports, or association with known malicious activity. Coverage and freshness vary significantly across providers.
VPN, Tor, hosting, and proxy indicators
Flags indicating whether the IP is associated with a VPN exit node, Tor relay, hosting provider, residential proxy network, or mobile proxy service. These are probabilistic signals, not definitive classifications.
IP geolocation does not establish a person's precise location. Network classification tells you about the IP block, not the individual using it.
Why residential proxy detection matters
Residential proxy networks route traffic through IP addresses assigned to consumer broadband connections. From a network-classification perspective, this traffic looks like it originates from a genuine household. Standard hosting or data-center detection does not identify it.
Residential proxies have legitimate uses: privacy tools, market research, ad verification, and geographic content access. They are also used to obscure the origin of automated activity, bypass rate limits, and make distributed attacks appear to come from many different locations.
Not all residential proxy traffic involves compromised devices. Some residential proxy networks operate with the consent of device owners. Do not assume that a residential proxy flag means a device has been hijacked—it means the IP is being used as a proxy endpoint, which warrants additional scrutiny in context.
| IP context | Description | Limitations | Signal value |
|---|---|---|---|
| Residential | Consumer broadband or mobile IP assigned to a household | Can be routed through residential proxy networks; does not confirm a legitimate user | Residential proxy flag adds context; classification alone is insufficient |
| Hosting / data center | IP assigned to a cloud provider, VPS, or data-center block | Easier to identify; legitimate users may also use cloud-hosted tools | Stronger automation signal when combined with high velocity or new accounts |
| Mobile network | IP assigned by a mobile carrier, often shared via CGNAT | Many users share a single IP; blocking by IP affects multiple users | Carrier-grade NAT means shared IPs are common; use with caution as a standalone signal |
Where it helps
IP signals are most useful when assessed alongside other evidence. Shared networks, privacy services, and mobile CGNAT mean that IP alone is rarely sufficient for a high-confidence decision.
Bot signup investigations
Identifying patterns of registrations from hosting IPs, known proxy networks, or unusual geographic distributions.
Suspicious login activity
Flagging logins from IPs inconsistent with a user's established location or network history.
Lead and affiliate screening
Identifying traffic from proxy networks or data centers that may indicate synthetic or incentivized activity.
Promotional abuse
Detecting distributed claim attempts that use residential proxies to appear as distinct users.
SMS verification abuse
Identifying high-velocity OTP requests from proxy or hosting IPs as part of SMS pumping investigations.
Payment-risk assessment
Flagging transactions where the IP location is inconsistent with the billing address or established account behavior.
IP signals should be assessed with other evidence, especially where customers share networks, use VPNs for legitimate reasons, or access your service from mobile connections.
What to evaluate in a provider
Residential and mobile-proxy coverage, data freshness, and the handling of uncertain results vary significantly. These are the practical questions to ask.
| Criterion | Questions to ask |
|---|---|
| Residential and mobile-proxy coverage | What proportion of known residential proxy IPs does the provider detect? How is mobile proxy coverage handled? |
| Data freshness | How frequently is the database updated? How quickly are newly identified proxy IPs added? |
| Reputation versus network classification | Does the provider distinguish between network classification (residential, hosting) and reputation signals (observed abuse)? Are these returned separately? |
| Reasons returned with classifications | Does the provider explain why an IP is flagged, or only return a score or binary flag? |
| False positives and uncertain results | What is the false-positive rate for residential proxy detection? How are uncertain results handled? |
| Country and network performance | How does coverage and accuracy vary across your key markets? Are there known gaps? |
| Lookup latency | What is the typical API response time for real-time lookups? |
| Pricing and commercial commitments | What is the per-lookup cost? Are there volume minimums, overage charges, or contract requirements? |
How to run a useful evaluation
Use a representative sample that reflects your actual traffic mix—not just flagged or suspicious events. A sample skewed toward known bad traffic will overstate detection rates.
Where available, use known outcomes to assess accuracy. Record relevant event timestamps: network assignments and proxy observations can change, and a current lookup may not reflect what was true at the time of the original event.
Compare providers on the same agreed scope. Differences in sample, timing, or evaluation criteria make provider comparisons unreliable. IFD can help structure a consistent evaluation.
Initial results may be available as soon as the next business day after we receive and validate your sample. We confirm timing and any provider charges before testing begins. A small sample does not establish production accuracy.
Common questions
See which IP signals improve your decisions.
IFD coordinates evaluations with suitable providers and helps you understand the results—with no evaluation coordination fee.
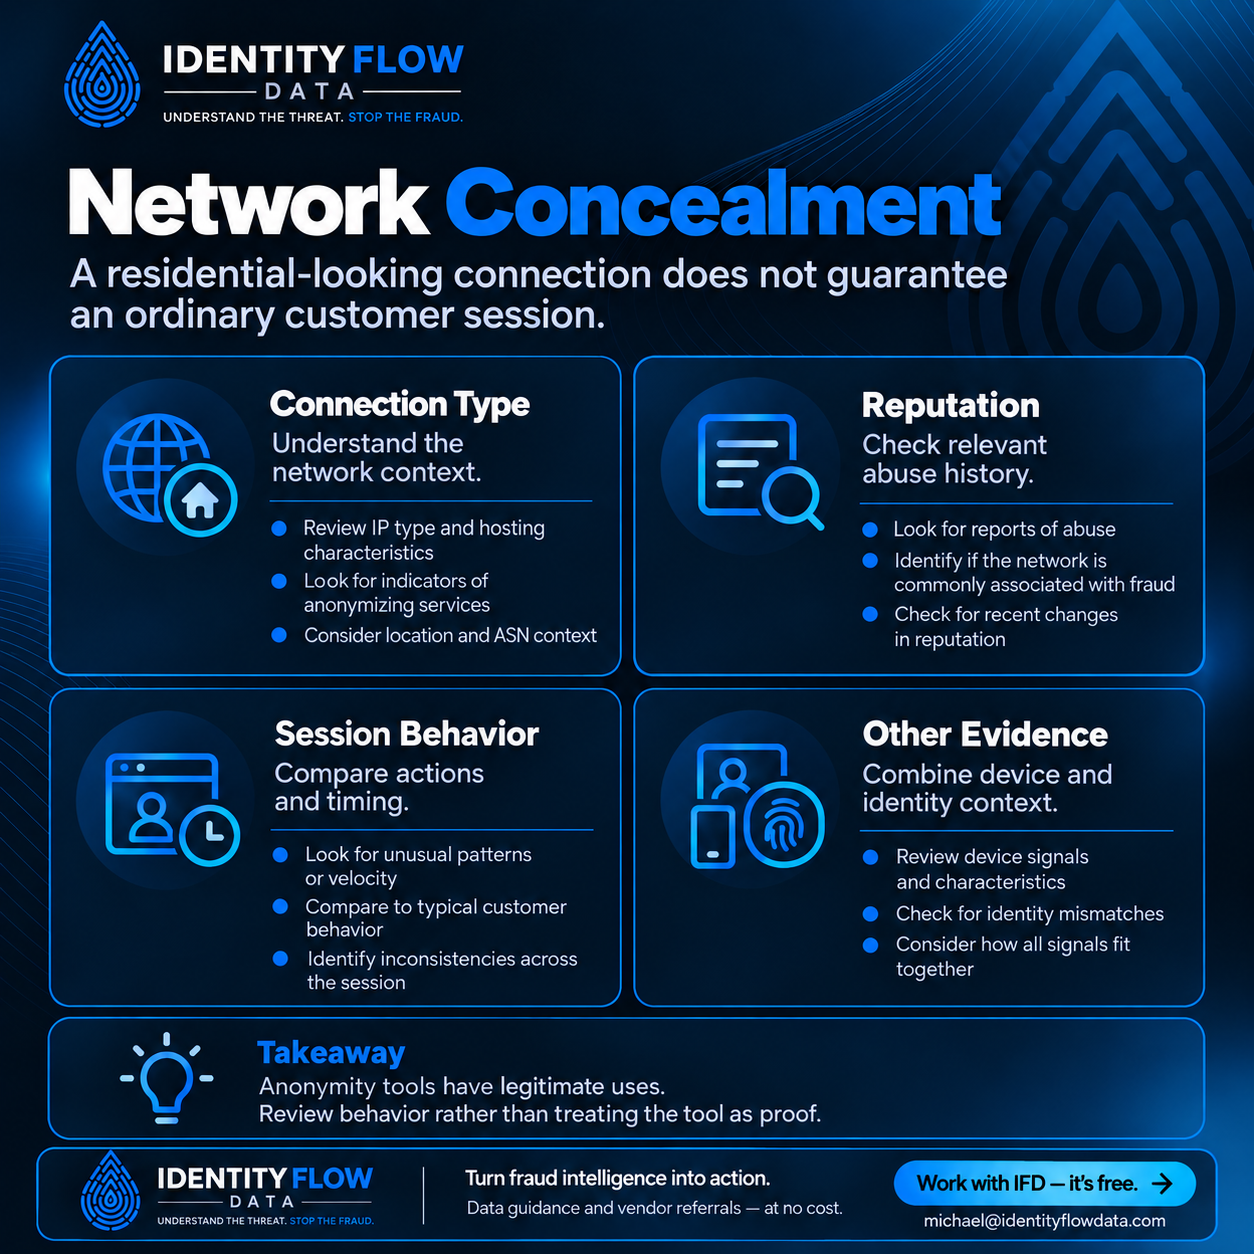
Connect the signals with the decision
Proxies, VPNs, Tor, and changing IP addresses can obscure connections between events. Their meaning depends on the activity around them.
- Connection Type: Understand the network context
- Reputation: Check relevant abuse history
- Session Behavior: Compare actions and timing
- Other Evidence: Combine device and identity context
Review a useful example
Choose a confirmed case and a comparable legitimate journey. Record what evidence was available at the decision point, what action followed and what was learned afterward. Compare how an additional signal would have changed the review, including cases where it would have added unnecessary friction.
Keep the interpretation proportionate
Anonymity tools have legitimate uses. Review behavior rather than treating the tool as proof.
Location signals and access decisions
Network location is one input. Assess it alongside session behavior, device context, and the specific action being reviewed. A mismatch between claimed and observed location is worth noting; it is not by itself evidence of intent.
Choose your starting point with IFD.
Evaluate your fraud data
Discuss a sample evaluation of relevant fraud and identity signals. No IFD coordination fee; scope and any provider charges agreed first.
Request a Data EvaluationUnderstand your business’s exposure
Request a scoped review of relevant underground activity and fraud techniques involving your business. No customer dataset required.
Request a Free Exposure ScanThere is no advisory fee for buyers. IFD is compensated by participating providers when a qualifying purchase results from a referral. We explain applicable arrangements upfront. Any provider testing or product charges are confirmed before you proceed.