
Duplicate Accounts and Multi-Accounting: How to Evaluate the Signals
Multiple accounts from the same person are not always abuse. A user who creates a second account after forgetting their password, or a household where two people share a device, can produce the same signals as a coordinated account-farming operation. Evaluating multi-accounting requires distinguishing patterns that indicate abuse from those that have legitimate explanations.
Written by Michael Joseph, Founder of Identity Flow Data
Michael has 10+ years of experience in fraud prevention, identity intelligence, and enterprise risk technology.
Last updated: September 2026
Legitimate multiple accounts versus abusive account creation
Legitimate reasons for multiple accounts include forgotten credentials, shared devices in a household, separate personal and business accounts, and testing by developers or QA teams. Abusive multi-accounting involves creating accounts specifically to exploit policies—claiming multiple signup bonuses, circumventing bans, farming referral rewards, or accumulating accounts for later resale or coordinated use.
The distinction is not always clear from signals alone. A shared IP address or device does not prove abuse—it may reflect a household, a workplace, or a shared network. The combination of signals, the velocity of account creation, and the downstream behavior of the accounts provide more context than any single indicator.
RELATED READING
- Duplicate account creation often shares signals with bot-driven signups. How to Detect Bot Signups and Fake Registrations covers related account-creation abuse patterns.
- Device signals can help identify returning actors across newly created accounts. Device Risk Intelligence explains what fingerprinting can and cannot establish.
- Residential proxies are commonly used to mask coordinated account creation across multiple IPs. Residential Proxy Detection: What Fraud Teams Should Evaluate covers what IP intelligence providers can and cannot establish.
Account-linkage evidence: what each signal can and cannot establish
The following evidence types are commonly used to assess account linkage. Each has meaningful limitations. Reliable decisions combine multiple signals with documented business policy.
| Evidence type | What it can help assess | Important limitation | Example proportionate response |
|---|---|---|---|
| Reused email address | Whether the same address appears across multiple accounts | Plus-addressing, dots, and aliases mean one person can have many apparent email addresses; shared addresses are also common | Flag for review if combined with velocity or other signals; do not reject on this basis alone |
| Reused phone number | Whether the same number is associated with multiple accounts | Shared household phones, number recycling by carriers, and porting mean one number may legitimately appear across accounts | Assess alongside account creation timing and other identifiers |
| Reused address or identity attributes | Whether the same physical address or identity elements appear across accounts | Households, businesses, and shared accommodation mean address reuse is common and not inherently suspicious | Consider in combination with velocity and downstream behavior |
| IP and network context | Whether accounts originate from the same IP, IP range, or network type | Shared IPs are common in households, workplaces, and shared networks; a single IP is not evidence of abuse | Note as one signal; investigate if combined with device and identity patterns |
| Device-environment assessment | Whether the current environment shows automation, emulator, location manipulation, or other risk indicators | Virtual machines, emulators, and privacy tools have legitimate uses; environment risk does not confirm the same person returned | Combine with identity and behavioral signals; apply proportionate friction rather than automatic rejection |
| Payment or transaction patterns | Whether the same payment instrument or transaction pattern appears across accounts | Shared cards within a household or business are common; payment reuse alone does not establish abuse | Investigate if combined with incentive-seeking behavior and other linkage signals |
| Behavioral timing and velocity | Whether accounts were created or used in patterns inconsistent with organic activity | Promotional events, app launches, and referral campaigns can produce genuine velocity spikes | Calibrate thresholds against your environment; review outliers rather than applying blanket blocks |
| Referral or promotion relationship | Whether accounts are linked through referral codes or promotional claims | Legitimate referral programmes produce clusters of linked accounts by design | Assess whether the referral relationship is consistent with programme terms and downstream engagement |
| Identity element reuse across accounts | Whether the same name, date of birth, or other identity attribute appears across multiple accounts with different contact details | Common names and shared household identity data can produce false matches | Look for corroborating patterns; document the basis for any action taken |
| Email or phone linked to different names | Whether a contact detail is associated with multiple distinct identities | Name changes, nicknames, and shared contact details have legitimate explanations | Assess velocity and source context; one instance may not warrant action |
| Repeated address or contact-data mismatches | Whether submitted identity elements are inconsistent with each other or with verification results | Recent moves, name changes, and partial form completion can produce apparent mismatches | Flag for manual review if multiple fields are inconsistent across linked accounts |
| Application or registration velocity across connected identifiers | Whether multiple accounts are being created rapidly using linked contact details, devices, or IPs | Legitimate bulk registration by businesses or developers can produce similar patterns | Investigate source and referral context; assess whether volume aligns with expected activity |
| Identity data inconsistent with account behavior or verification results | Whether submitted identity elements conflict with downstream verification or observed account activity | Verification data quality varies; inconsistencies may reflect data errors rather than misuse | Use as corroborating evidence alongside other signals; document the basis for any action |
Identity reuse, recycled data, and coordinated account activity
Some abuse attempts rely on identity and contact details that may have been exposed, recycled, mismatched, or reused across unrelated applications. The useful question is not whether one data point looks unusual. It is whether multiple signals indicate that the submitted identity, contact details, device environment, network context, timing, and account behavior warrant a proportionate next step.
Reused emails, phones, addresses, identity attributes, or payment patterns can indicate account linkage, coordinated activity, promotional abuse, or possible identity misuse. A single individual may legitimately use multiple accounts or share a device, address, or payment method with others. Patterns such as one email associated with multiple names, repeated contact details across accounts, inconsistent identity elements, unusual account velocity, or repeated registration submissions may warrant additional review. They do not independently establish fraud or identity theft.
More meaningful risk assessment looks for corroboration: repeated identity mismatches, unusual velocity, first-interaction environment risk, device manipulation indicators, network context, and inconsistent behavior over time. The appropriate response may be to allow, limit a benefit, request additional verification, hold for review, or investigate—depending on the business policy and evidence available. Testing a representative sample can help identify whether identity reuse, mismatches, velocity, and first-interaction risk signals may add useful context to your existing workflow.
Investigating duplicate accounts or multi-accounting?
IFD helps you identify the right signals and evaluate providers suited to your account-abuse challenges.
Device risk without recognition
Device recognition—linking a current session to a previously observed device—is useful for identifying accounts that share a device. But recognition is not the only device capability relevant to multi-accounting.
Device-risk assessment evaluates the current environment for signs of manipulation, automation, and suspicious configurations. A device that has never been seen before can still show emulator indicators, automation signals, or inconsistent attributes that suggest it is not a genuine user device. This is particularly relevant for new account creation, where there is no prior device history to compare against.
Evaluating both capabilities separately—risk assessment of the current environment, and recognition of returning devices—gives a more complete picture than relying on either alone.
A practical evaluation approach
When evaluating multi-accounting signals, a structured approach helps distinguish patterns that warrant action from those with legitimate explanations:
- 1Define what counts as a duplicate. Establish clear criteria: same email, same phone, same device, same IP within a time window, or some combination. Document the criteria so that reviews are consistent.
- 2Assess the combination of signals. A single shared signal—one IP address, one device—may have a legitimate explanation. Multiple shared signals across the same accounts, combined with velocity and incentive-seeking patterns, build a stronger case for investigation.
- 3Review downstream behavior. Accounts that claim an incentive and then show no further engagement, or that are used in coordinated patterns, provide behavioral evidence to complement signal-based assessment.
- 4Calibrate thresholds against outcomes. Set review thresholds based on observed outcomes in your environment, not on generic benchmarks. What constitutes a suspicious velocity in one product may be normal in another.
Multi-accounting evaluation checklist
- Define criteria for what constitutes a duplicate or linked account
- Check for repeated contact identifiers across accounts, including variations
- Assess account creation velocity by IP, device, and contact detail
- Evaluate device-environment risk signals, including on first-seen devices
- Review downstream behavior: incentive claims, engagement, and account activity
- Calibrate review thresholds against observed outcomes in your environment
Common questions
Does a shared IP address prove multi-accounting abuse?
No. Shared IP addresses are common in households, workplaces, universities, and shared networks. A shared IP is a signal to consider alongside other evidence—not a standalone reason to flag or restrict accounts.
Can device intelligence detect multi-accounting on first-seen devices?
Yes, in part. Device recognition links sessions to previously observed devices, which is useful for identifying shared devices. But device-risk assessment can also evaluate the current environment for automation, emulator, and manipulation signals—even on a device that has never been seen before. Both capabilities are relevant to multi-accounting.
How do I distinguish a legitimate second account from abuse?
Context matters. A second account created months after the first, from a different device and IP, with no incentive claim, is less concerning than two accounts created within minutes from the same device, both claiming a signup bonus. Assess the combination of signals and downstream behavior rather than applying a single threshold.
Identity Flow Data helps teams evaluate the signals relevant to duplicate-account and multi-accounting challenges, scope representative tests, and compare providers—with no advisory fee for buyers.
Ready to scope an account-abuse evaluation?
IFD coordinates evaluations and helps you interpret results. No advisory fee for buyers.
RELATED ARTICLES
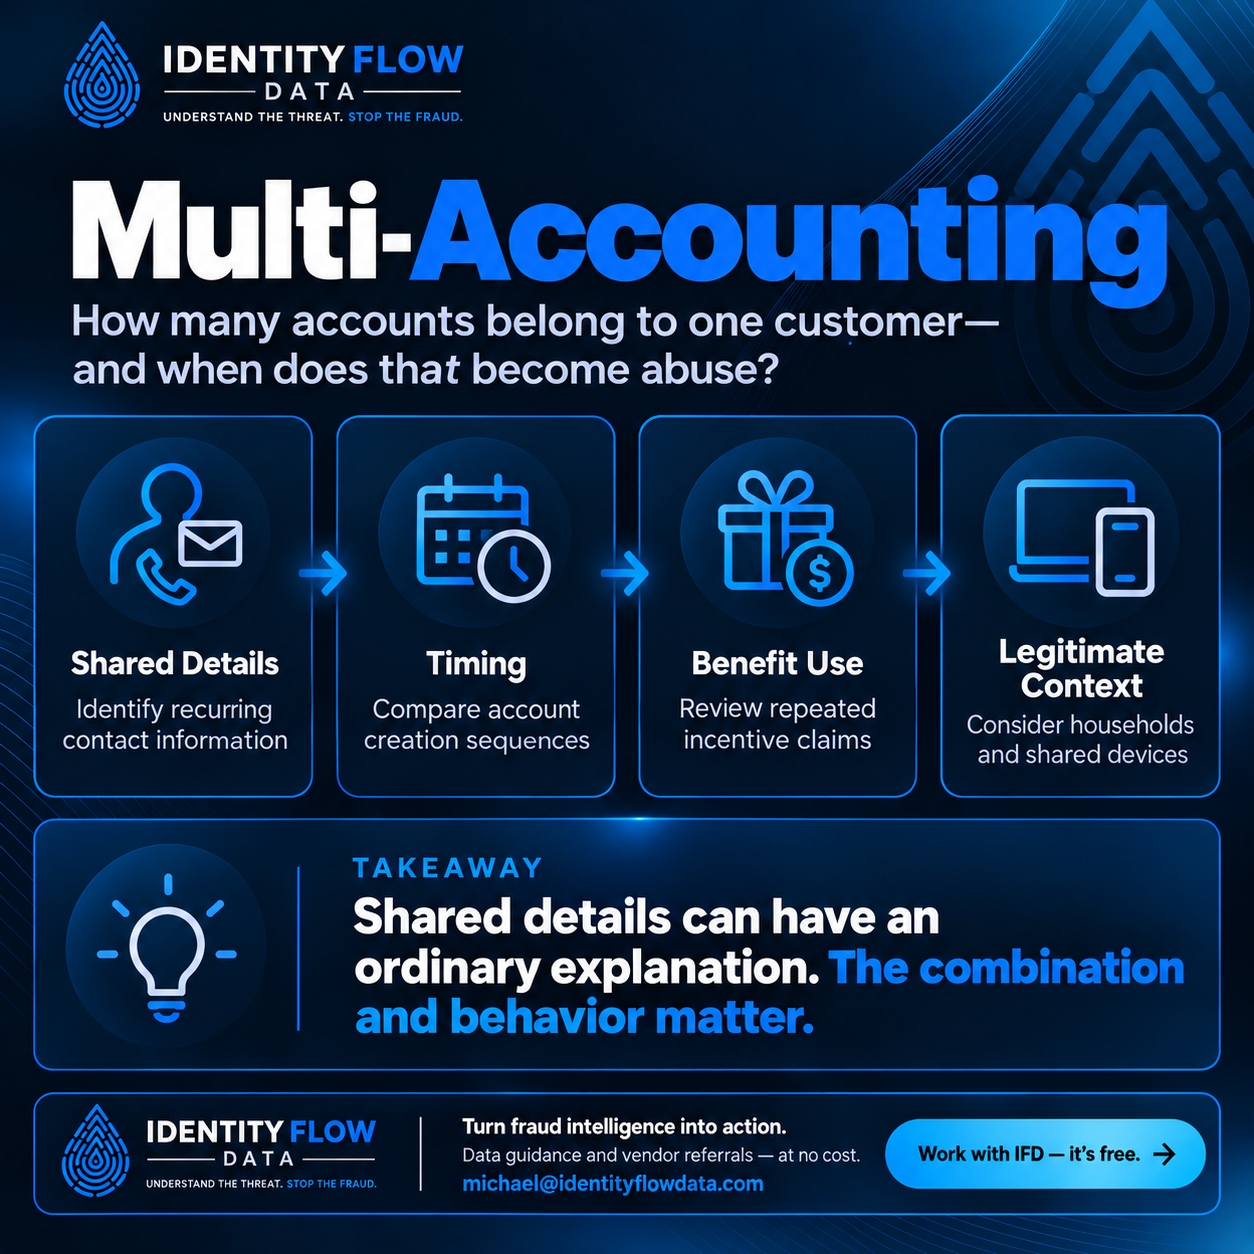
Connect the signals with the decision
The useful question is what connected accounts are doing, particularly when limited benefits or incentives are involved.
- Shared Details: Identify recurring contact information
- Timing: Compare account creation sequences
- Benefit Use: Review repeated incentive claims
- Legitimate Context: Consider households and shared devices
Review a useful example
Choose a confirmed case and a comparable legitimate journey. Record what evidence was available at the decision point, what action followed and what was learned afterward. Compare how an additional signal would have changed the review, including cases where it would have added unnecessary friction.
Keep the interpretation proportionate
Shared details can have an ordinary explanation. The combination and behavior matter.
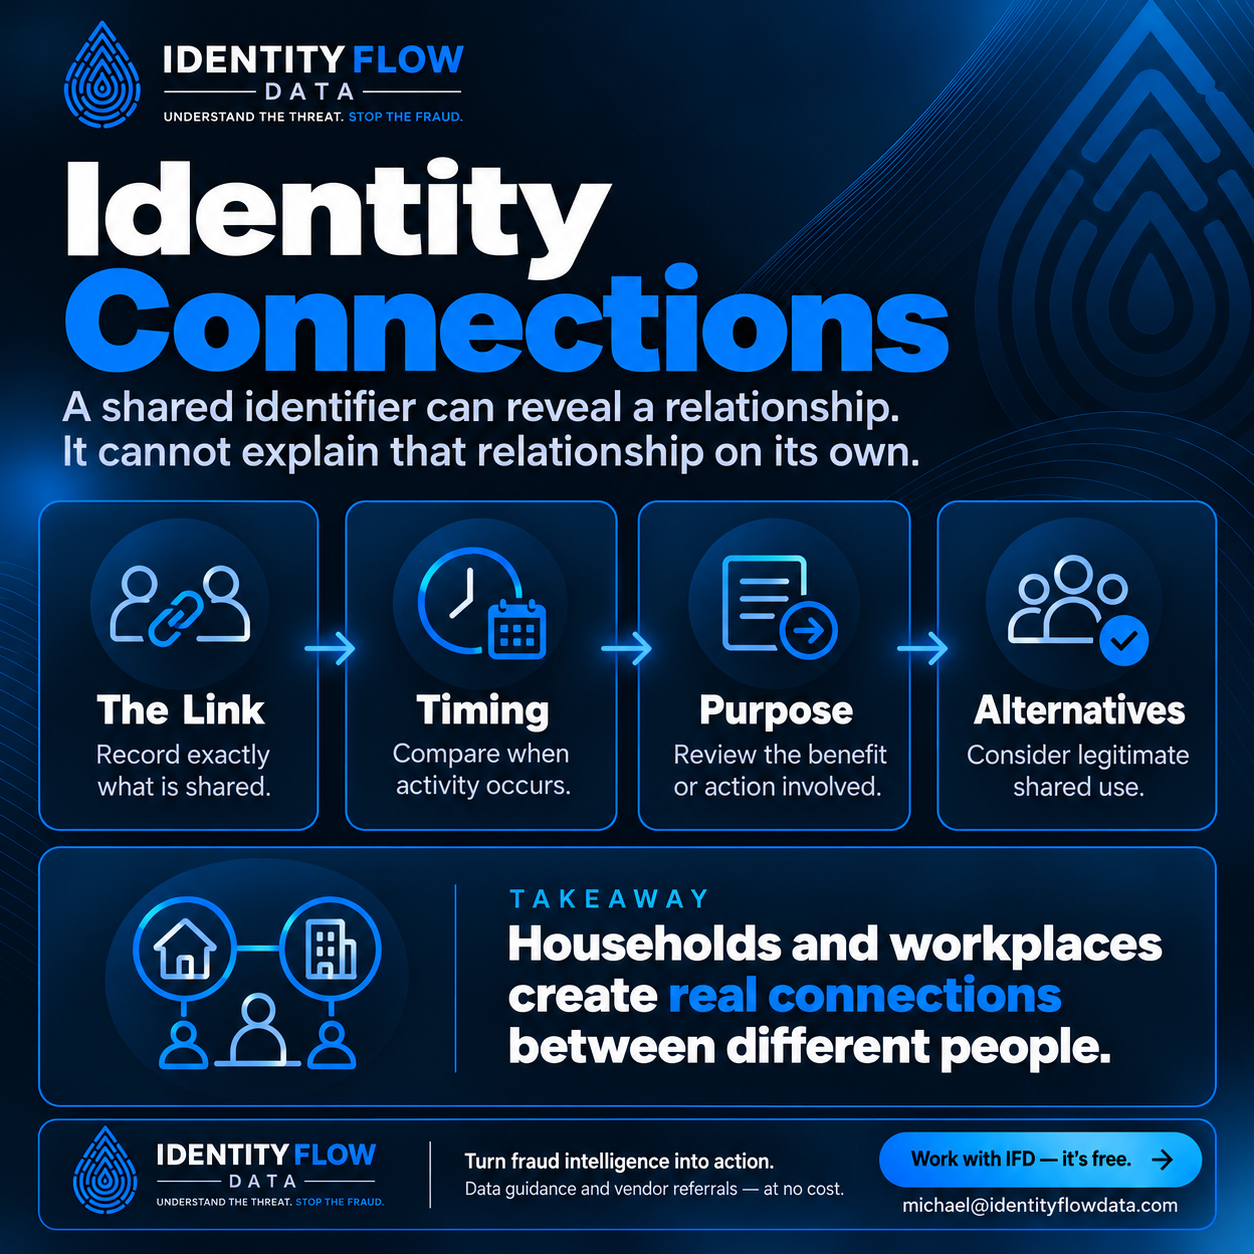
Identity connections: record the link before interpreting it
A shared identifier establishes an observed connection. Assess its timing, the action involved and legitimate alternatives before inferring coordination. Keep the relationship evidence available to the reviewer rather than collapsing it into an unexplained label.
Choose your starting point with IFD.
Understand your business’s exposure
Request a scoped review of relevant underground activity and fraud techniques involving your business. No customer dataset required.
Request a Free Exposure ScanEvaluate your fraud data
Discuss a sample evaluation of relevant fraud and identity signals. No IFD coordination fee; scope and any provider charges agreed first.
Request a Data EvaluationThere is no advisory fee for buyers. IFD is compensated by participating providers when a qualifying purchase results from a referral. We explain applicable arrangements upfront. Any provider testing or product charges are confirmed before you proceed.