
Email Validation and Fraud-Risk Intelligence
Understand whether an email address is deliverable and what additional risk context it provides. IFD helps you evaluate email-validation and risk-intelligence capabilities against your signup, transaction or account-review workflow. Review coverage, freshness, false positives and the value added beyond your existing controls. An email-risk signal alone does not establish identity or prove fraud.
What email intelligence can tell you
Email checks address different questions. Understanding which question each check answers helps you avoid drawing conclusions the data does not support.
| Check | Can reveal | Cannot establish |
|---|---|---|
| Syntax and formatting | Confirm the address is correctly formatted and that the domain portion is structurally valid. | Confirm the domain is active, the mailbox exists, or that anyone uses it. |
| Domain mail acceptance | Indicate whether the domain is configured to receive email. | Confirm a specific mailbox exists. Catch-all domains accept mail for any address, including fabricated ones. |
| Mailbox-level deliverability | Assess whether a specific mailbox is likely to receive messages, where the provider supports this check. Providers use various methods to assess deliverability without necessarily sending a real test message. | Guarantee delivery or confirm the mailbox is actively used. Results are uncertain for catch-all domains and some providers. |
| Disposable-email classification | Identify addresses from services designed for temporary or anonymous use. | Establish that the user is fraudulent. Legitimate users use disposable addresses for privacy. |
| Domain reputation and risk signals | Provide context about the domain's history and observed associations. | Confirm the intent of the person using the address. Reputation signals reflect observed patterns, not individual intent. |
| First-seen date | Indicate when the provider first observed the address in its dataset. | Establish when the mailbox was created. Provider first-seen dates reflect dataset coverage, not mailbox age. |
A deliverable address is not the same as a trustworthy user. Email checks provide context about the address—not about the person using it.
Disposable and temporary email detection
Disposable-email services provide addresses that can be used once or for a short period, then discarded. They are commonly used to bypass email verification, claim multiple trial offers, or register without providing a permanent contact address.
Detection uses maintained domain intelligence and other provider-specific methods to identify addresses associated with temporary-email services. Coverage varies across providers—a domain one provider classifies as disposable may be unknown to another. New disposable services appear regularly, so no dataset is complete.
Legitimate users also use disposable addresses for privacy reasons. A disposable classification is a signal to consider alongside other evidence, not a standalone reason to reject a registration.
Domain reputation and email-risk indicators
Beyond deliverability and disposable classification, some providers offer domain reputation scores, email-risk indicators, or signals derived from observed patterns across their dataset. These may include associations with spam, phishing, or abuse activity.
Risk signals reflect patterns observed in a provider's data. They do not independently confirm that a specific user is fraudulent. Evaluate what each signal actually measures and how it is derived before incorporating it into a decision.
Combining email signals with IP, phone, device, and account context produces a more complete picture than any single check. An address that passes all email checks may still be associated with suspicious network or device activity.
What to evaluate in a provider
Email intelligence implementations vary significantly in coverage, freshness, and what each signal actually measures. These are the practical questions to ask.
| Area | Question to ask |
|---|---|
| Coverage and catch-all handling | How does the provider handle catch-all domains? Does it return a definitive result, an uncertain result, or skip the check? |
| Data freshness | How frequently is the provider's dataset updated? What is the typical lag between a domain change and a reflected result? |
| Unknown and inconclusive results | How are unknown or unverifiable addresses handled? Does the API distinguish between 'unknown' and 'invalid'? |
| Disposable domain coverage | How many disposable domains does the provider track? How quickly are new services added? |
| First-seen date interpretation | What does the provider's first-seen date actually measure? Is it first observation in their dataset, or something else? How does dataset coverage affect the date returned? |
| Risk signal explanations | What explanations accompany a risk score or flag? Are contributing factors returned, or only a summary? |
| Latency and integration | What is the expected API response time for real-time checks? What are the integration requirements? |
| Pricing and volume | What is the pricing model? Are there volume minimums, overage charges, or per-check fees for specific signal types? |
How to scope a representative sample evaluation
A useful email data evaluation uses a sample that reflects your actual traffic—a mix of addresses from recent signups, including both accepted and rejected registrations where available.
IFD agrees on sample scope, required fields, evaluation criteria, and secure transfer before testing begins. Initial results may be available as soon as the next business day after we receive and validate your sample, subject to provider and scope.
Compare providers on the same agreed sample. Differences in how providers handle catch-all domains, unknown results, and disposable classification can significantly affect apparent accuracy.
Ready to scope an email data evaluation?
IFD helps agree on sample scope, criteria, and secure transfer before testing begins.
RELATED READING
Common questions
Find out which email signals are useful for your business.
IFD coordinates email data evaluations and helps you interpret the results in the context of your specific use case—with no advisory fee for buyers.
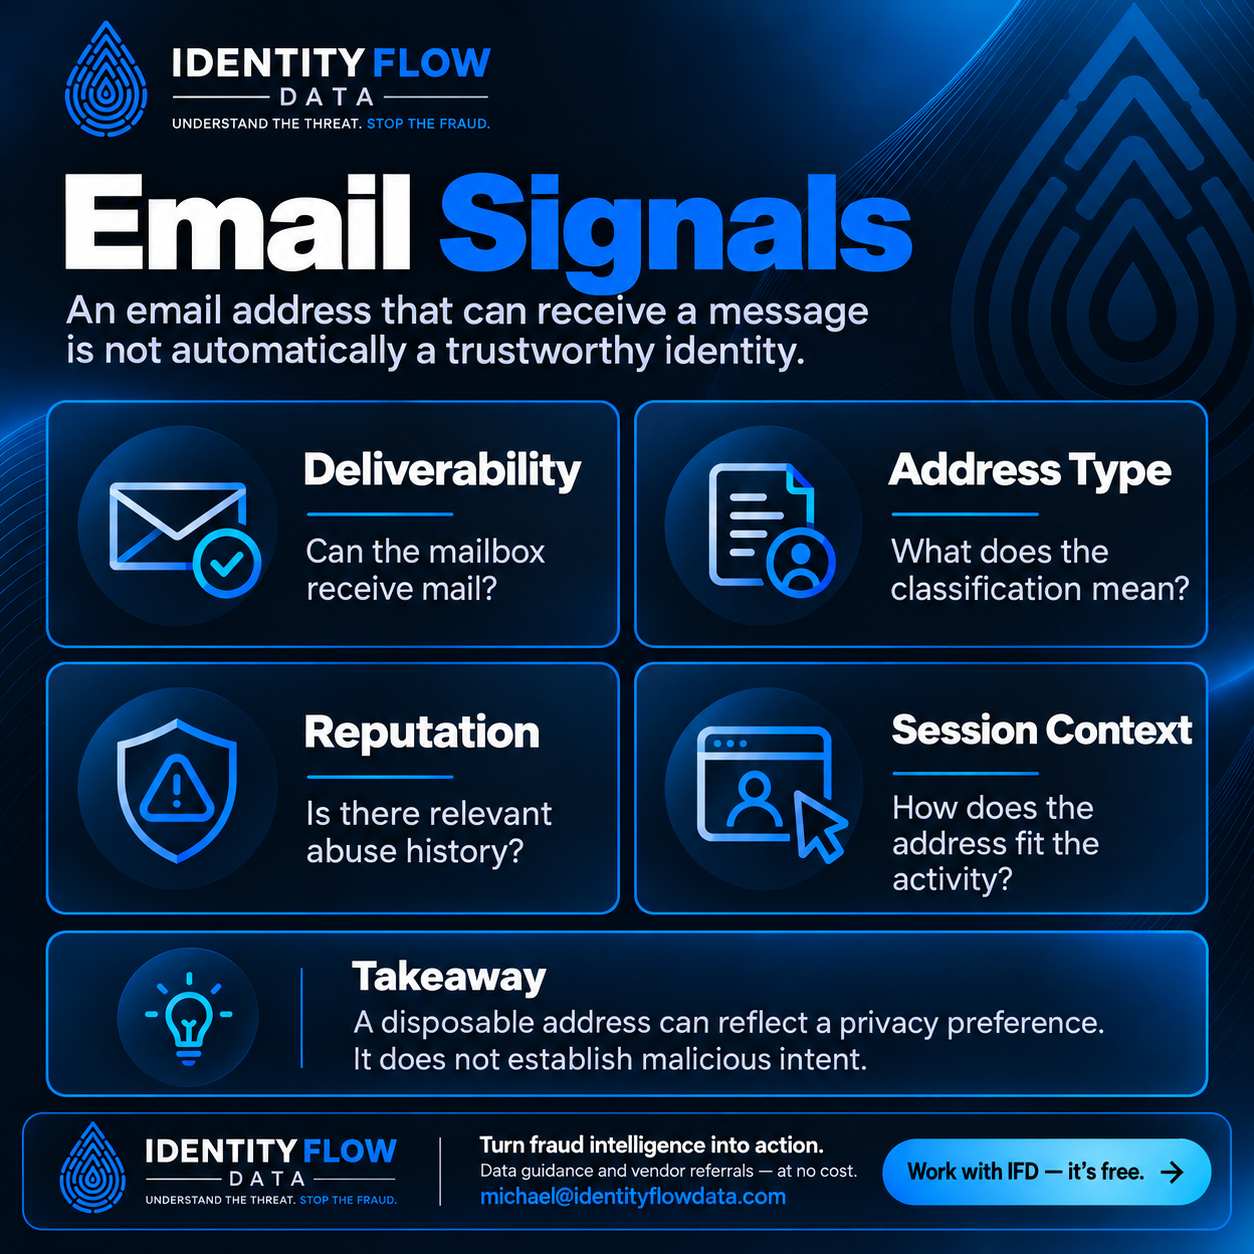
Connect the signals with the decision
Deliverability, disposable status, reputation, and compromise evidence answer different questions.
- Deliverability: Can the mailbox receive mail?
- Address Type: What does the classification mean?
- Reputation: Is there relevant abuse history?
- Session Context: How does the address fit the activity?
Review a useful example
Choose a confirmed case and a comparable legitimate journey. Record what evidence was available at the decision point, what action followed and what was learned afterward. Compare how an additional signal would have changed the review, including cases where it would have added unnecessary friction.
Keep the interpretation proportionate
A disposable address can reflect a privacy preference. It does not establish malicious intent.
Choose your starting point with IFD.
Evaluate your fraud data
Discuss a sample evaluation of relevant fraud and identity signals. No IFD coordination fee; scope and any provider charges agreed first.
Request a Data EvaluationUnderstand your business’s exposure
Request a scoped review of relevant underground activity and fraud techniques involving your business. No customer dataset required.
Request a Free Exposure ScanThere is no advisory fee for buyers. IFD is compensated by participating providers when a qualifying purchase results from a referral. We explain applicable arrangements upfront. Any provider testing or product charges are confirmed before you proceed.